Application Logging Vocabulary Cheat Sheet / 应用日志词汇速查表
This document proposes a standard vocabulary for logging security events. The intent is to simplify monitoring and alerting such that, assuming developers trap errors and log them using this vocabulary, monitoring and alerting would be improved by simply keying on these terms.
本文档提出了一个用于记录安全事件的标准化词汇表。目的是简化监控和警报,以便假设开发人员捕获错误并使用此词汇表进行记录,通过关注这些术语,监控和警报将得到改善。
Overview / 概述
Each year IBM Security commissions the Ponemon Institute to survey companies around the world for information related to security breaches, mitigation, and the associated costs; the result is called the Cost of a Data Breach Report.
每年IBM安全部门委托Ponemon研究所对全球公司进行有关安全漏洞、缓解措施及其相关成本的信息调查;结果被称为《数据泄露成本报告》。
In addition to the millions of dollars lost due to breaches the report finds that the mean time to identify a breach continues to hover around 200 days. Clearly our ability to monitor applications and alert on anomalous behavior would improve our time to identify and mitigate an attack against our applications.
除了因漏洞造成的数百万美元损失外,报告发现平均发现漏洞时间继续徘徊在200天左右。显然,我们监控应用程序并针对异常行为发出警报的能力将提高我们识别和缓解针对我们应用程序的攻击的时间。
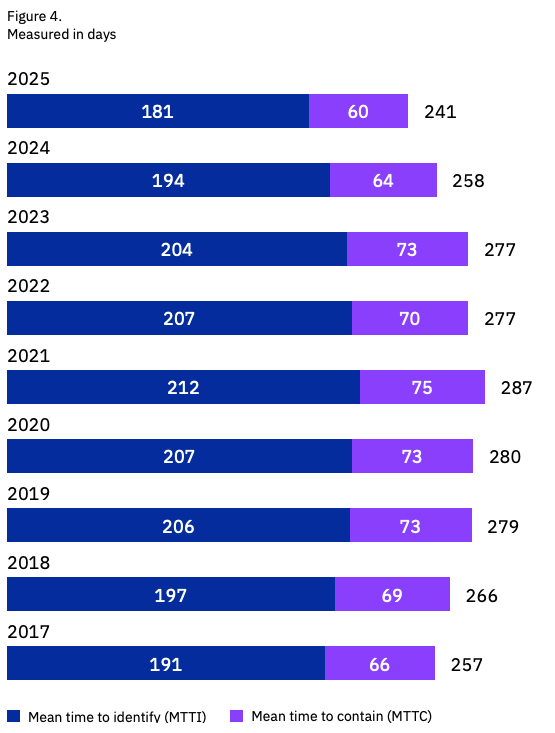
IBM Cost of a Data Breach Report 2025, Fig.4, pg.12
中文:IBM 数据泄露成本报告 2025,图4,第12页
This logging standard would seek to define specific keywords which, when applied consistently across software, would allow groups to simply monitor for these events terms across all applications and respond quickly in the event of attack.
此日志标准将寻求定义特定的关键词,当这些关键词在软件中得到一致应用时,将允许团队在所有应用程序中简单地监控这些事件术语,并在攻击发生时迅速响应。
Assumptions / 假设
- Observability/SRE groups must support the use of this standard and encourage developers to use it
中文:可观测性/SRE 团队必须支持使用此标准,并鼓励开发者使用它 - Incident Response must either ingest this data OR provide a means by which other monitoring teams can send a notification of alert, preferably programmatically.
中文:事件响应必须摄取这些数据或者提供一种方式,让其他监控团队可以发送警报通知,最好是程序化的方式。 - Architects must support, adopt, and contribute to this standard
中文:架构师必须支持、采用并贡献于这个标准。 - Developers must embrace this standard and begin to implement (requires knowledge and intent to understand potential attacks and trap those errors in code).
中文:开发者必须接受这个标准并开始实施(需要知识和意图来理解潜在的攻击并在代码中捕获这些错误)。
Getting Started / 入门指南
As a reminder, the goal of logging is to be able to alert on specific security events. Of course, the first step to logging these events is good error handling, if you're not trapping the events, you don't have an event to log.
提醒一下,日志记录的目标是能够对特定的安全事件进行警报。当然,记录这些事件的第一步是良好的错误处理,如果你没有捕获事件,你就没有可以记录的事件。
Identifying Events / 识别事件
In order to better understand security event logging a good high-level understanding of threat modeling would be helpful, even if it's a simple approach of:
为了更好地理解安全事件日志记录,对威胁建模有一个良好的高级理解会有所帮助,即使它只是一个简单的步骤:
- What could go wrong?
中文:可能出错的地方?**
- Orders: could someone order on behalf of another?
中文:订单:有人能代表别人下单吗? - Authentication: could I log in as someone else?
中文:身份验证:我能以别人的身份登录吗? - Authorization: could I see someone else' account?
中文:授权:我能查看别人的账户吗?
- What would happen if it did?
中文:如果这样做了会发生什么?**
- Orders: I've placed an order on behalf of another... to an abandoned warehouse in New Jersey. Oops.
中文:订单:我代表别人下了一个订单...寄到了新泽西州的一个废弃仓库。哎呀。 - Then I bragged about it on 4Chan.
中文:然后我在4Chan上炫耀了这件事。 - Then I told the New York Times about it.
中文:然后我告诉了《纽约时报》。
- Who might intend to do this?
中文:谁可能有意这样做?**
- Intentional attacks by hackers.
中文:黑客的有意攻击。 - An employee "testing" how things work.
中文:一名员工“测试”事物的工作方式。 - An API coded incorrectly doing things the author did not intend.
中文:一个编码错误的API执行了作者不希望的操作。
Implementation / 实现
Some languages have libraries which ease the job of adopting this logging vocabulary in applications:
一些语言有库,可以简化在应用程序中采用这种日志词汇的工作:
- Python: lucabello/owasp-logger
- C#/.NET: byteguard-hq/byteguard-security-logger
- Python / Java / Go / Node.js: thatsjet/security_event_logger
Format / 格式
NOTE: All dates should be logged in ISO 8601 format WITH UTC offset to ensure maximum portability
注意:所有日期应以ISO 8601格式带有UTC偏移量记录,以确保最大程度的可移植性
{
    "datetime": "2021-01-01T01:01:01-0700",
    "appid": "foobar.netportal_auth",
    "event": "AUTHN_login_success:joebob1",
    "level": "INFO",
    "description": "User joebob1 login successfully",
    "useragent": "Mozilla/5.0 (Macintosh; Intel Mac OS X 10_14_6) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/78.0.3904.108 Safari/537.36",
    "source_ip": "165.225.50.94",
    "host_ip": "10.12.7.9",
    "hostname": "portalauth.foobar.com",
    "protocol": "https",
    "port": "440",
    "request_uri": "/api/v2/auth/",
    "request_method": "POST",
    "region": "AWS-US-WEST-2",
    "geo": "USA"
}
The Vocabulary / 词汇表
What follows are the various event types that should be captured. For each event type there is a prefix like "authn" and additional data that may be included for that event.
以下是要捕获的各种事件类型。对于每种事件类型,都有一个如“authn”的前缀,以及可能包含在该事件中的附加数据。
Portions of the full logging format are included for example, but a complete event log should follow the format above.
Note on Data Privacy:
All fields logged after event type should be considered optional. Businesses implementing this logging method should consider value of the fields being logged vs. responsibility as a data steward for the data logged. For example: logging user IP address may be useful for detection and response, but may be considered personally identifiable information when combined with other data and subject to regulation or deletion requests.
Authentication [AUTHN]
authn_login_success[:userid]
Description All login events should be recorded including success.
Level: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_login_success:joebob1",
    "level": "INFO",
    "description": "User joebob1 login successfully",
    ...
}
authn_login_successafterfail[:userid,retries] / 认证登录成功(失败后)[:用户ID,重试次数]
Description The user successfully logged in after previously failing.
描述 用户在之前失败后成功登录。
Level: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_login_successafterfail:joebob1,2",
    "level": "INFO",
    "description": "User joebob1 login successfully",
    ...
}
authn_login_fail[:userid] / 认证登录失败[:用户ID]
Description All login events should be recorded including failure.
描述 应记录所有登录事件,包括失败事件。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_login_fail:joebob1",
    "level": "WARN",
    "description": "User joebob1 login failed",
    ...
}
authn_login_fail_max[:userid,maxlimit(int)] / 认证登录失败最大次数[:用户ID,最大限制(int)]
Description All login events should be recorded including failure.
描述 应记录所有登录事件,包括失败事件。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_login_fail_max:joebob1,3",
    "level": "WARN",
    "description": "User joebob1 reached the login fail limit of 3",
    ...
}
authn_login_lock[:userid,reason] / 认证登录锁定[:用户ID,原因]
Description When the feature exists to lock an account after x retries or other condition, the lock should be logged with relevant data.
描述 当存在在x次重试或其他条件下锁定账户的功能时,应记录锁定事件的相关数据。
Level: WARN
级别:警告
Reasons:
原因:
- maxretries: The maximum number of retries was reached
中文:maxretries: 重试次数已达到最大值 - suspicious: Suspicious activity was observed on the account
中文:suspicious: 账户上观察到可疑活动 - customer: The customer requested their account be locked
中文:customer: 客户请求锁定账户 - other: Other
中文:other: 其他
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_login_lock:joebob1,maxretries",
    "level": "WARN",
    "description": "User joebob1 login locked because maxretries exceeded",
    ...
}
authn_password_change[:userid]
Description Every password change should be logged, including the userid that it was for.
描述 每次密码更改都应记录,包括更改的用户的用户ID。
Level: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_password_change:joebob1",
    "level": "INFO",
    "description": "User joebob1 has successfully changed their password",
    ...
}
authn_password_change_fail[:userid]
Description
An attempt to change a password that failed. May also trigger other events such as authn_login_lock.
描述 密码更改尝试失败。也可能触发其他事件,如 authn_login_lock。
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_password_change_fail:joebob1",
    "level": "CRITICAL",
    "description": "User joebob1 failed to change their password",
    ...
}
authn_impossible_travel[:userid,region1,region2]
Description When a user is logged in from one city and suddenly appears in another, too far away to have traveled in a reasonable timeframe, this often indicates a potential account takeover.
描述 当用户从一个城市登录,突然出现在另一个城市,距离太远,在合理时间内无法旅行,这通常表明可能存在账户接管风险。
Level:: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_impossible_travel:joebob1,US-OR,CN-SH",
    "level": "CRITICAL",
    "description": "User joebob1 has accessed the application in two distant cities at the same time",
    ...
}
authn_token_created[:userid, entitlement(s)]
Description When a token is created for service access it should be recorded
描述 当为服务访问创建令牌时,应记录该令牌。
Level:: INFO
级别: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "aws.foobar.com",
    "event": "authn_token_created:app.foobarapi.prod,create,read,update",
    "level": "INFO",
    "description": "A token has been created for app.foobarapi.prod with create,read,update",
    ...
}
authn_token_revoked[:userid,tokenid] / 认证令牌已撤销[:userid,tokenid]
Description A token has been revoked for the given account.
描述 给定账户的令牌已被撤销。
Level:: INFO
级别: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "aws.foobar.com",
    "event": "authn_token_revoked:app.foobarapi.prod,xyz-abc-123-gfk",
    "level": "INFO",
    "description": "Token ID: xyz-abc-123-gfk was revoked for user app.foobarapi.prod",
    ...
}
authn_token_reuse[:userid,tokenid] / 认证令牌重用[:userid,tokenid]
Description A previously revoked token was attempted to be reused.
描述 尝试重用之前已撤销的令牌。
Level:: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "aws.foobar.com",
    "event": "authn_token_reuse:app.foobarapi.prod,xyz-abc-123-gfk",
    "level": "CRITICAL",
    "description": "User app.foobarapi.prod attempted to use token ID: xyz-abc-123-gfk which was previously revoked",
    ...
}
authn_token_delete[:appid] / 认证令牌删除[:appid]
Description When a token is deleted it should be recorded
描述 当令牌被删除时,应记录该操作
Level:: WARN
级别:: 警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authn_token_delete:foobarapi",
    "level": "WARN",
    "description": "The token for foobarapi has been deleted",
    ...
}
Authorization [AUTHZ] / 授权 [AUTHZ]
authz_fail[:userid,resource] / 授权失败[:userid,资源]
Description An attempt was made to access a resource which was unauthorized
描述 尝试访问未经授权的资源
Level:: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authz_fail:joebob1,resource",
    "level": "CRITICAL",
    "description": "User joebob1 attempted to access a resource without entitlement",
    ...
}
authz_change[:userid,from,to] / 授权变更[:userid,从,到]
Description The user or entity entitlements was changed
描述 用户或实体的权限已更改
Level:: WARN
级别:: 警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authz_change:joebob1,user,admin",
    "level": "WARN",
    "description": "User joebob1 access was changed from user to admin",
    ...
}
authz_admin[:userid,event] / 授权管理[:userid,事件]
Description All activity by privileged users such as admin should be recorded.
描述 应记录所有由具有特权的用户(如管理员)执行的活动
Level:: WARN
级别:: 警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "authz_admin:joebob1,user_privilege_change",
    "level": "WARN",
    "description": "Administrator joebob1 has updated privileges of user foobarapi from user to admin",
    ...
}
Encryption/Decryption [CRYPT]
crypt_decrypt_fail[userid] / 加密解密失败[userid]
Description Failure to perform encryption and decryption could be simply due to a system error, or it may be related to authorization failures where a user lacks permissions on the related data.
描述 执行加密和解密失败可能是由于系统错误,也可能与授权失败有关,其中用户对相关数据缺乏权限
Level:: WARN
级别:: 警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "crypt_decrypt_fail:joebob1",
    "level": "WARN",
    "description": "User joebob1 was unable to perform decryption" + err,
    ...
}
crypt_encrypt_fail[userid] / 加密失败[用户ID]
Description Failure to perform encryption and decryption could be simply due to a system error, or it may be related to authorization failures where a user lacks permissions on the related data.
描述 执行加密和解密失败可能是由于系统错误,也可能与授权失败有关,其中用户对相关数据缺乏权限
Level:: WARN
级别:: 警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "crypt_encrypt_fail:joebob1",
    "level": "WARN",
    "description": "User joebob1 was unable to perform encryption" + err,
    ...
}
Excessive Use [EXCESS] / 过度使用[过度]
excess_rate_limit_exceeded[userid,max] / excess_rate_limit_exceeded[用户ID,最大值]
Description Expected service limit ceilings should be established and alerted when exceeded, even if simply for managing costs and scaling.
描述 应当建立并触发超出预期服务限制的警报,即使只是为了管理成本和扩展。
Level:: WARN
级别:: 警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "excess_rate_limit_exceeded:app.foobarapi.prod,100000",
    "level": "WARN",
    "description": "User app.foobarapi.prod has exceeded max:100000 requests",
    ...
}
excess_sessions_exceeded[userid,max] / excess_sessions_exceeded[用户ID,最大值]
Description When a user exceeds the maximum number of concurrent sessions allowed it should be logged. An unusually high concurrent-session count can indicate credential sharing or account takeover.
描述 当用户超出允许的最大并发会话数时,应记录下来。异常高的并发会话数可能表明凭证共享或账户接管。
Level:: WARN
级别:: 警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "excess_sessions_exceeded:app.foobarapi.prod,5",
    "level": "WARN",
    "description": "User app.foobarapi.prod exceeded the max of 5 concurrent sessions",
    ...
}
File Upload [UPLOAD] / 文件上传[上传]
upload_complete[userid,filename,type] / upload_complete[用户ID,文件名,类型]
Description On successful file upload the first step in the validation process is that the upload has completed.
描述 文件上传成功后,验证过程的第一步是上传已完成。
Level:: INFO
级别: INFO
Example:
    {
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "upload_complete:joebob1,user_generated_content.png,PNG",
    "level": "INFO",
    "description": "User joebob1 has uploaded user_generated_content.png",
    ...
}
upload_stored[filename,from,to]
Description One step in good file upload validation is to move/rename the file and when providing the content back to end users, never reference the original filename in the download. This is true both when storing in a filesystem as well as in block storage.
描述 良好的文件上传验证步骤之一是移动/重命名文件,并且在将内容返回给最终用户时,永远不要引用原始文件名进行下载。这在存储在文件系统以及块存储中都是正确的。
Level:: INFO
级别: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "upload_stored:user_generated_content.png,kjsdhkrjhwijhsiuhdf000010202002",
    "level": "INFO",
    "description": "File user_generated_content.png was stored in the database with key abcdefghijk101010101",
    ...
}
upload_validation[filename,(virusscan|imagemagick|...):(FAILED|incomplete|passed)]
Description All file uploads should have some validation performed, both for correctness (is in fact of file type x), and for safety (does not contain a virus).
描述 所有文件上传都应该进行一些验证,包括正确性(确实是文件类型x)和安全(不包含病毒)。
Level:: INFO|CRITICAL
级别:INFO|CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "upload_validation:filename,virusscan:FAILED",
    "level": "CRITICAL",
    "description": "File user_generated_content.png FAILED virus scan and was purged",
    ...
}
upload_delete[userid,fileid]
Description When a file is deleted for normal reasons it should be recorded.
描述 当文件因正常原因被删除时,应该进行记录。
Level:: INFO
级别: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "upload_delete:joebob1,",
    "level": "INFO",
    "description": "User joebob1 has marked file abcdefghijk101010101 for deletion.",
    ...
}
Input Validation [INPUT] / 输入验证 [INPUT]
input_validation_fail:[(fieldone,fieldtwo...),userid]
Description When input validation fails on the server-side it must either be because a) sufficient validation was not provided on the client, or b) client-side validation was bypassed. In either case it's an opportunity for attack and should be mitigated quickly.
描述 当服务器端输入验证失败时,通常是因为客户端没有提供足够的验证,或者客户端验证被绕过。在任一情况下,这都是一个攻击的机会,应该迅速缓解。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "input_validation_fail:(zip,date_of_birth),joebob1",
    "level": "WARN",
    "description": "User joebob1 submitted data that failed validation.",
    ...
}
input_validation_discrete_fail[:field,userid]
Description When server-side validation of a value against a discrete list of options (e.g. drop down list, radio buttons) fails, it is a strong indication of malicious activity as this indicates the client-side code has been tampered with.
描述 当服务器端对值与离散选项列表(例如下拉列表、单选按钮)的验证失败时,这是一个强烈的恶意活动迹象,因为这表明客户端代码已被篡改。
Level: WARN
级别:警告
Example:
{
    "datetime": "2021-02-01T08:30:00-0500",
    "appid": "foobar.netportal_auth",
    "event": "input_validation_discrete_fail:country,joebob1",
    "level": "WARN",
    "description": "User joebob1 submitted an invalid value for the 'country' field.",
    ...
}
Malicious Behavior [MALICIOUS] / 恶意行为 [MALICIOUS]
malicious_excess_404:[userid|IP,useragent]
Description When a user makes numerous requests for files that don't exist it often is an indicator of attempts to "force-browse" for files that could exist and is often behavior indicating malicious intent.
描述 当用户多次请求不存在的文件时,这通常表明试图“强制浏览”可能存在的文件,这通常是表明恶意意图的行为。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_excess404:123.456.789.101,M@l1c10us-Hax0rB0t0-v1",
    "level": "WARN",
    "description": "A user at 123.456.789.101 has generated a large number of 404 requests.",
    ...
}
malicious_extraneous:[userid|IP,inputname,useragent]
Description When a user submits data to a backend handler that was not expected it can indicate probing for input validation errors. If your backend service receives data it does not handle or have an input for this is an indication of likely malicious abuse.
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_extraneous:dr@evil.com,creditcardnum,Mozilla/5.0 (X11; Linux x86_64; rv:10.0) Gecko/20100101 Firefox/10.0",
    "level": "CRITICAL",
    "description": "User dr@evil.com included field creditcardnum in the request which is not handled by this service.",
    ...
}
malicious_attack_tool:[userid|IP,toolname,useragent]
Description When obvious attack tools are identified either by signature or by user agent they should be logged.
For example, the tool "Nikto" leaves behind its user agent by default with a string like "Mozilla/5.00 (Nikto/2.1.6) (Evasions:None) (Test:Port Check)"
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_attack_tool:127.0.0.1,nikto,Mozilla/5.00 (Nikto/2.1.6) (Evasions:None) (Test:Port Check)",
    "level": "CRITICAL",
    "description": "Attack traffic indicating use of Nikto coming from 127.0.0.1",
    ...
}
malicious_sqli:[userid|IP,parameter,ruleid,useragent]
Description When request input matches a SQL injection (SQLi) signature or heuristic, log the suspected attempt. Configure blocking under a tested policy and tune false positives for the application; a detection match is not proof of exploitation. Use parameterized queries and the other primary SQL injection defenses regardless of detection rules.
NOTE: Logging the payload is dangerous and may result in log injection. Prefer recording a detection rule ID / category and the parameter name over logging the full payload.
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_sqli:127.0.0.1,search,SQLI-UNION,Mozilla/5.0 (X11; Linux x86_64; rv:10.0) Gecko/20100101 Firefox/10.0",
    "level": "CRITICAL",
    "description": "Request from 127.0.0.1 contained a SQL injection pattern (rule SQLI-UNION) in parameter 'search'.",
    ...
}
malicious_cors:[userid|IP,useragent,referer] / 恶意跨源资源共享:[用户ID|IP,用户代理,引用者]
Description When attempts are made from unauthorized origins they should of course be blocked, but also logged whenever possible. Even if we block an illegal cross-origin request the fact that the request is being made could be an indication of attack.
描述 当来自未经授权的源发起尝试时,当然应该被阻止,但在可能的情况下也应记录。即使我们阻止了非法的跨源请求,但请求正在被发起的事实本身可能就是攻击的迹象。
NOTE: Did you know that the word "referer" is misspelled in the original HTTP specification? The correct spelling should be "referrer" but the original typo persists to this day and is used here intentionally.
注意:你知道吗?在原始HTTP规范中,“referer”一词拼写错误。正确的拼写应该是“referrer”,但原始的误拼至今仍存在,并且在此处故意使用。
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_cors:127.0.0.1,Mozilla/5.0 (X11; Linux x86_64; rv:10.0) Gecko/20100101 Firefox/10.0,attack.evil.com",
    "level": "CRITICAL",
    "description": "An illegal cross-origin request from 127.0.0.1 was referred from attack.evil.com"
    ...
}
malicious_direct_reference:[userid|IP, useragent] / 恶意直接引用:[用户ID|IP,用户代理]
Description A common attack against authentication and authorization is to directly access an object without credentials or appropriate access authority. Failing to prevent this flaw used to be one of the OWASP Top Ten called Insecure Direct Object Reference. Assuming you've correctly prevented this attack, logging the attempt is valuable to identify malicious users.
描述 对身份验证和授权的一种常见攻击是直接访问一个对象,而不需要凭证或适当的访问权限。未能防止这种缺陷曾经是OWASP十大之一,称为不安全的直接对象引用。假设你已经正确地阻止了这种攻击,记录尝试对于识别恶意用户是有价值的。
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_direct_reference:joebob1, Mozilla/5.0 (X11; Linux x86_64; rv:10.0) Gecko/20100101 Firefox/10.0",
    "level": "CRITICAL",
    "description": "User joebob1 attempted to access an object to which they are not authorized",
    ...
}
malicious_csrf:[userid|IP] / 恶意CSRF:[用户ID|IP]
Description When a state-changing request arrives without a valid anti-CSRF token (or with a mismatched token, Origin, or Referer) it may indicate a cross-site request forgery attempt. Block the request and log the attempt. See the OWASP Cross-Site Request Forgery Prevention Cheat Sheet for token and Origin/Referer validation guidance.
描述 当一个状态改变请求到达时没有有效的反CSRF令牌(或者令牌、源或引用者不匹配)可能表明了跨站请求伪造尝试。阻止请求并记录尝试。请参阅OWASP跨站请求伪造预防备忘单以获取令牌和源/引用者验证的指导。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_csrf:joebob1",
    "level": "WARN",
    "description": "A state-changing request from joebob1 was missing a valid anti-CSRF token",
    ...
}
malicious_csp_violation:[userid|IP,effective_directive,blocked_uri,useragent] / 恶意内容安全策略违规:[用户ID|IP,有效指令,被阻止的URI,用户代理]
Description When a browser reports a Content-Security-Policy violation to your report endpoint, log the violation. In Report-Only mode this is high-noise — browser extensions and injected third-party scripts trigger benign violations — so WARN is appropriate; promote to CRITICAL only if you treat enforced-mode blocks as attack signal.
NOTE: CSP report fields such as document-uri, referrer, and blocked-uri are URL-valued (see the W3C Content Security Policy Level 3 violation report definition) and routinely contain full URLs whose query strings carry session or reset tokens. Strip the query string/fragment before logging, and prefer the effective-directive + blocked-uri (origin+path) over the full report body to avoid a secondary sensitive-data or log-injection risk.
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "malicious_csp_violation:203.0.113.7,script-src,https://foobar.com/dashboard,Mozilla/5.0",
    "level": "WARN",
    "description": "A CSP violation for directive script-src was reported by a browser at 203.0.113.7",
    ...
}
MCP Servers [MCP]
This section focuses on concerns related to the use of MCP servers either within productivity applications, or at the enterprise level.
mcp_prompt_injection[:userid]
Description When an MCP client or server detects indicators of prompt injection (for example, instructions to ignore system/developer messages, attempts to override tool policies, requests to reveal secrets, or attempts to coerce tool calls outside of the intended task), block or constrain the action and log the event for investigation.
NOTE: Avoid logging the full prompt/tool I/O. Prefer logging a detection category or rule ID, the target tool/server, and request identifiers to support triage without creating a secondary sensitive-data or log-injection risk.
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.cooldevapp_mcp_toolname",
    "event": "mcp_prompt_injection:joebob1",
    "level": "WARN",
    "description": "A possible prompt injection has occurred",
    ...
}
mcp_resource_exhaustion[:userid]
Description When an MCP client or server detects a request pattern intended to exhaust resources (for example, unusually large prompts, repeated retries, tool-call loops, or other behavior that drives excessive token usage and cost), terminate or throttle the activity and log the attempt.
描述 当 MCP 客户端或服务器检测到旨在耗尽资源的请求模式(例如,异常大的提示、重复重试、工具调用循环或其他导致过度使用令牌和产生成本的行為),终止或限制该活动并记录尝试。
NOTE: Avoid logging full prompts or tool inputs/outputs. Prefer logging measured usage (tokens in/out), policy thresholds, request identifiers, and the tool/model involved.
注意:避免记录完整的提示或工具输入/输出。建议记录测量使用情况(令牌输入/输出)、策略阈值、请求标识符以及涉及的工具/模型。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.cooldevapp_mcp_toolname",
    "event": "mcp_resource_exhaustion:joebob1",
    "level": "WARN",
    "description": "Request blocked due to token budget overrun (tokens_in=18240, tokens_out=0, budget=8000)",
    ...
}
mcp_tool_poisoning[:userid]
Description When an MCP client or server detects that a tool may be malicious or tampered with (for example, unexpected tool changes, signature/hash verification failures, suspicious tool metadata, or a tool sourced from an agent/tool marketplace with minimal validation), block or quarantine the tool and log the attempt.
描述 当 MCP 客户端或服务器检测到工具可能存在恶意或被篡改(例如,意外的工具更改、签名/哈希验证失败、可疑的工具元数据或来自具有最少验证的代理/工具市场的工具),阻止或隔离该工具并记录尝试。
NOTE: Tool ecosystems and agent marketplaces can enable rapid proliferation of third-party tools with relatively low validation. An internal marketplace or hashed allowlist for approved tools is highly recommended.
注意:工具生态系统和代理市场可以促进第三方工具的快速传播,而验证相对较低。强烈建议使用内部市场或经过验证的工具的散列允许列表。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.cooldevapp_mcp_toolname",
    "event": "mcp_tool_poisoning:joebob1",
    "level": "WARN",
    "description": "Tool execution blocked (tool=\"calendar_sync\", source=\"https://marketplace.example/tools/calendar_sync\", version=\"2.4.1\", signature=\"missing\", policy=\"allowlist_required\")",
    ...
}
Privilege Changes [PRIVILEGE] / 权限变更 [PRIVILEGE]
This section focuses on object privilege changes such as read/write/execute permissions or objects in a database having authorization meta-information changed.
本节重点介绍对象权限变更,例如读取/写入/执行权限或数据库中具有授权元信息的对象。
Changes to user/account are covered in the User Management section.
用户/账户的变更请参阅用户管理部分。
privilege_permissions_changed:[userid,file|object,fromlevel,tolevel] / 权限变更:[用户ID,文件|对象,从级别,到级别]
Description Tracking changes to objects to which there are access control restrictions can uncover attempt to escalate privilege on those files by unauthorized users.
描述 跟踪对存在访问控制限制的对象的更改可以发现未经授权用户试图提升对这些文件的权限的企图。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "permissions_changed:joebob1, /users/admin/some/important/path,0511,0777",
    "level": "WARN",
    "description": "User joebob1 changed permissions on /users/admin/some/important/path",
    ...
}
Sensitive Data Changes [DATA] / 敏感数据变更 [DATA]
It's not necessary to log or alert on changes to all files, but in the case of highly sensitive files or data it is important that we monitor and alert on changes.
不需要对所有文件的更改进行日志记录或警报,但在高度敏感的文件或数据的情况下,我们监控和警报更改是很重要的。
sensitive_create:[userid,file|object] / 敏感创建:[用户ID,文件|对象]
Description When a new piece of data is created and marked as sensitive or placed into a directory/table/repository where sensitive data is stored, that creation should be logged and reviewed periodically.
描述 当创建新的数据并标记为敏感或放置到存储敏感数据的目录/表/仓库中时,应该记录该创建并定期审查。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sensitive_create:joebob1, /users/admin/some/important/path",
    "level": "WARN",
    "description": "User joebob1 created a new file in /users/admin/some/important/path",
    ...
}
sensitive_read:[userid,file|object] / 敏感读取:[用户ID,文件|对象]
Description All data marked as sensitive or placed into a directory/table/repository where sensitive data is stored should be have access logged and reviewed periodically.
描述 所有标记为敏感或放置到存储敏感数据的目录/表/仓库中的数据应该记录访问并定期审查。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sensitive_read:joebob1, /users/admin/some/important/path",
    "level": "WARN",
    "description": "User joebob1 read file /users/admin/some/important/path",
    ...
}
sensitive_update:[userid,file|object] / 敏感更新:[用户ID,文件|对象]
Description All data marked as sensitive or placed into a directory/table/repository where sensitive data is stored should be have updates to the data logged and reviewed periodically.
描述 所有标记为敏感或存储在存储敏感数据的目录/表/存储库中的数据,应记录数据更新并定期审查。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sensitive_update:joebob1, /users/admin/some/important/path",
    "level": "WARN",
    "description": "User joebob1 modified file /users/admin/some/important/path",
    ...
}
sensitive_delete:[userid,file|object] / 敏感删除:[用户ID,文件|对象]
Description Log and periodically review deletion events for sensitive files and data. Record the action and object identifier without copying the sensitive contents into the log. Retain the underlying data according to the applicable information-retention requirements (NIST SI-12), then securely dispose of it and retained copies when no longer needed (SI-12(3)). Keep the deletion audit record according to the log retention and disposal requirements; recording a deletion event does not itself require archiving the deleted file.
描述 记录并定期审查敏感文件和数据的删除事件。记录操作和对象标识符,但不将敏感内容复制到日志中。根据适用的信息保留要求(NIST SI-12),保留底层数据,然后在不再需要时安全地销毁并保留副本(SI-12(3))。根据日志保留和处置要求保留删除审计记录;记录删除事件本身不需要存档已删除的文件。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sensitive_delete:joebob1, /users/admin/some/important/path",
    "level": "WARN",
    "description": "User joebob1 deleted file /users/admin/some/important/path",
    ...
}
Sequence Errors [SEQUENCE] / 序列错误 [SEQUENCE]
Also called a business logic attack, if a specific path is expected through a system and an attempt is made to skip or change the order of that path it could indicate malicious intent.
也称为业务逻辑攻击,如果系统期望通过特定路径,并且尝试跳过或更改该路径的顺序,这可能表明恶意意图。
sequence_fail:[userid] / 序列失败:[用户ID]
Description When a user reaches a part of the application out of sequence it may indicate intentional abuse of the business logic and should be tracked.
描述 当用户达到应用程序中的非顺序部分时,这可能表明有意滥用业务逻辑,应予以跟踪。
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sequence_fail:joebob1",
    "level": "CRITICAL",
    "description": "User joebob1 has reached a part of the application out of the normal application flow.",
    ...
}
Session Management [SESSION] / 会话管理 [SESSION]
session_created:[userid]
Description When a new authenticated session is created that session may be logged and activity monitored.
描述 当创建一个新的已验证会话时,该会话可能会被记录,并且活动会被监控。
Level: INFO
Example:
    {
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "session_created:joebob1",
    "level": "INFO",
    "description": "User joebob1 has started a new session",
    ...
}
session_renewed:[userid]
Description When a user is warned of session to be expired/revoked and chooses to extend their session that activity should be logged. Also, if the system in question contains highly confidential data then extending a session may require additional verification.
描述 当用户被警告会话即将过期/被撤销并选择延长会话时,该活动应该被记录。此外,如果涉及的系统包含高度机密数据,则延长会话可能需要额外的验证。
Level: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "session_renewed:joebob1",
    "level": "INFO",
    "description": "User joebob1 was warned of expiring session and extended.",
    ...
}
session_expired:[userid,reason]
Description When a session expires, especially in the case of an authenticated session or with sensitive data, then that session expiry may be logged and clarifying data included. The reason code may be any such as: logout, timeout, revoked, etc. Sessions should never be deleted but rather expired in the case of revocation requirement.
描述 当会话过期时,尤其是在已验证会话或敏感数据的情况下,该会话过期可能会被记录,并包含澄清数据。原因代码可以是任何此类,例如:登出、超时、撤销等。会话不应被删除,而是在撤销需求的情况下过期。
Level: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "session_expired:joebob1,revoked",
    "level": "INFO",
    "description": "User joebob1 session expired due to administrator revocation.",
    ...
}
session_logout:[userid]
Description
When a user explicitly logs out (as opposed to a timeout or administrative revocation) the event may be logged. This is a more explicit alternative to session_expired:[userid,logout] for systems that distinguish a user-initiated logout. Do not include the raw session ID or bearer token. If session correlation is needed, follow the Session Management logging guidance.
描述 当用户明确退出登录(与超时或管理员撤销不同)时,可能会记录此事件。这是针对区分用户主动退出登录的系统的一种更明确的替代方案,即 session_expired:[userid,logout]。不要包含原始会话ID或承载令牌。如果需要会话关联,请遵循会话管理日志记录指南。
Level: INFO
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "session_logout:joebob1",
    "level": "INFO",
    "description": "User joebob1 logged out",
    ...
}
session_use_after_expire:[userid]
Description In the case a user attempts to access systems with an expire session it may be helpful to log, especially if combined with subsequent login failure. This could identify a case where a malicious user is attempting a session hijack or directly accessing another person's machine/browser.
描述 如果用户尝试访问已过期的会话,记录此事件可能有所帮助,特别是如果与随后的登录失败结合使用。这可能会识别出恶意用户正在尝试会话劫持或直接访问他人的机器/浏览器的情况。
Level: CRITICAL
级别: CRITICAL
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "session_use_after_expire:joebob1",
    "level": "CRITICAL",
    "description": "User joebob1 attempted access after session expired.",
    ...
}
System Events [SYS] / 系统事件 [SYS]
sys_startup:[userid]
Description When a system is first started it can be valuable to log the startup, even if the system is serverless or a container, especially if possible to log the user that initiated the system.
描述 当系统首次启动时,记录启动事件可能很有价值,即使系统是无服务器或容器,尤其是如果可以记录启动系统的用户。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sys_startup:joebob1",
    "level": "WARN",
    "description": "User joebob1 spawned a new instance",
    ...
}
sys_shutdown:[userid]
Description When a system is shut down it can be valuable to log the event, even if the system is serverless or a container, especially if possible to log the user that initiated the system.
描述 当系统关闭时,记录事件可能很有价值,即使系统是无服务器或容器,尤其是如果可以记录启动系统的用户。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sys_shutdown:joebob1",
    "level": "WARN",
    "description": "User joebob1 stopped this instance",
    ...
}
sys_restart:[userid] / sys_restart:[用户ID]
Description When a system is restarted it can be valuable to log the event, even if the system is serverless or a container, especially if possible to log the user that initiated the system.
描述 当系统重启时,记录该事件可能很有价值,即使系统是无服务器或容器,尤其是如果可能记录启动系统的用户。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sys_restart:joebob1",
    "level": "WARN",
    "description": "User joebob1 initiated a restart",
    ...
}
sys_crash[:reason] / sys_crash[:原因]
Description If possible to catch an unstable condition resulting in the crash of a system, logging that event could be helpful, especially if the event is triggered by an attack.
描述 如果可能捕捉到导致系统崩溃的不稳定状态,记录该事件可能很有帮助,尤其是如果该事件是由攻击触发的。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sys_crash:outofmemory,
    "level": "WARN",
    "description": "The system crashed due to Out of Memory error.",
    ...
}
sys_monitor_disabled:[userid,monitor] / sys_monitor_disabled:[用户ID,监控器]
Description If your systems contain agents responsible for file integrity, resources, logging, virus, etc. it is especially valuable to know if they are halted and by whom.
描述 如果您的系统包含负责文件完整性、资源、日志、病毒等任务的代理,了解它们是否被停止以及由谁停止特别有价值。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sys_monitor_disabled:joebob1,crowdstrike",
    "level": "WARN",
    "description": "User joebob1 has disabled CrowdStrike",
    ...
}
sys_monitor_enabled:[userid,monitor] / sys_monitor_enabled:[用户ID,监控器]
Description If your systems contain agents responsible for file integrity, resources, logging, virus, etc. it is especially valuable to know if they are started again after being stopped, and by whom.
描述 如果您的系统包含负责文件完整性、资源、日志、病毒等任务的代理,了解它们在停止后是否重新启动,以及由谁启动特别有价值。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "sys_monitor_enabled:joebob1,crowdstrike",
    "level": "WARN",
    "description": "User joebob1 has enabled CrowdStrike",
    ...
}
User Management [USER] / 用户管理 [USER]
user_created:[userid,newuserid,attributes[one,two,three]]
Description When creating new users, logging the specifics of the user creation event is helpful, especially if new users can be created with administration privileges.
描述 当创建新用户时,记录用户创建事件的详细信息是有帮助的,特别是如果新用户可以拥有管理权限时。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "user_created:joebob1,user1,admin:create,update,delete",
    "level": "WARN",
    "description": "User joebob1 created user1 with admin:create,update,delete privilege attributes",
    ...
}
user_updated:[userid,onuserid,attributes[one,two,three]]
Description When updating users, logging the specifics of the user update event is helpful, especially if users can be updated with administration privileges.
描述 当更新用户时,记录用户更新事件的详细信息是有帮助的,特别是如果用户可以拥有管理权限时。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "user_updated:joebob1,user1,admin:create,update,delete",
    "level": "WARN",
    "description": "User joebob1 updated user1 with attributes admin:create,update,delete privilege attributes",
    ...
}
user_archived:[userid,onuserid]
Description It is always best to archive users rather than deleting, except where required. When archiving users, logging the specifics of the user archive event is helpful. A malicious user could use this feature to deny service to legitimate users.
描述 总是最好归档用户而不是删除,除非必要。当归档用户时,记录用户归档事件的详细信息是有帮助的。恶意用户可能会利用此功能拒绝合法用户的服务。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "user_archived:joebob1,user1",
    "level": "WARN",
    "description": "User joebob1 archived user1",
    ...
}
user_deleted:[userid,onuserid]
Description It is always best to archive users rather than deleting, except where required. When deleting users, logging the specifics of the user delete event is helpful. A malicious user could use this feature to deny service to legitimate users.
描述 始终建议归档用户而不是删除,除非必要。删除用户时,记录用户删除事件的详细信息是有帮助的。恶意用户可能会利用此功能拒绝合法用户的服务。
Level: WARN
级别:警告
Example:
{
    "datetime": "2019-01-01 00:00:00,000",
    "appid": "foobar.netportal_auth",
    "event": "user_deleted:joebob1,user1",
    "level": "WARN",
    "description": "User joebob1 has deleted user1",
    ...
}
Exclusions / 排除项
As important as what you DO log is what you DON'T log. Private or secret information, source code, keys, certs, etc. should never be logged.
记录什么与不记录什么同样重要。私人或机密信息、源代码、密钥、证书等不应被记录。
For comprehensive overview of items that should be excluded from logging, please see the OWASP Logging Cheat Sheet.
有关应从日志记录中排除的项目 comprehensive overview,请参阅 OWASP 日志记录作弊表。
References / 参考
- RFC 5424: The Syslog Protocol) (RFC 5424:系统日志协议)
- NIST SP 800-92: Guide to Computer Security Log Management) (NIST SP 800-92:计算机安全日志管理指南)